Security Operations
Block unsafe agent commands before they hit infrastructure, APIs, or sensitive files.
Pre-execution firewall and tamper-evident flight recorder for AI agents.
IronVise blocks risky tool calls, such as reading SSH keys outside the workspace or rm -rf /, before they run, and exports offline-verifiable audit certificates for EU AI Act Article 12 record-keeping (applies to Annex III high-risk systems from 2 December 2027) and ISO 42001 evidence.
Article 12 requires high-risk AI systems to keep automatic logs over their lifetime. It does not require those logs to be hard to edit afterwards. IronVise runs agent actions through policy checks and OS sandboxes and records every one in a hash-chained, Ed25519-signed ledger that a third party can verify offline - without your database, your keys, or your cooperation. Prototype; not independently audited.
It complements your sandbox rather than replacing it. Docker Sandboxes (sbx), Perplexity SPACE or E2B limit what an agent can reach once a command runs; IronVise decides whether the command runs at all and keeps a signed record a third party can check. Use both.
Built for teams running AI in high-risk workflows: security, compliance, platform engineering, and enterprise operations.
Use Cases
Block unsafe agent commands before they hit infrastructure, APIs, or sensitive files.
Produce tamper-evident evidence trails for internal and external audit requirements.
Show customers exactly what the agent attempted, what was blocked, and what actually executed.
Replay AI-assisted workflows with signed, hash-chained records for post-incident analysis.
Clarity first
IronVise is not a crypto trading product. Here, "ledger" means a tamper-evident audit log for AI agent behavior.
.elc certificates) for customers, auditors, and regulators.Flowchart
Every proposed action is checked before execution. Denied actions are blocked and recorded. Allowed actions execute and are sealed into cryptographic evidence.
See it in action
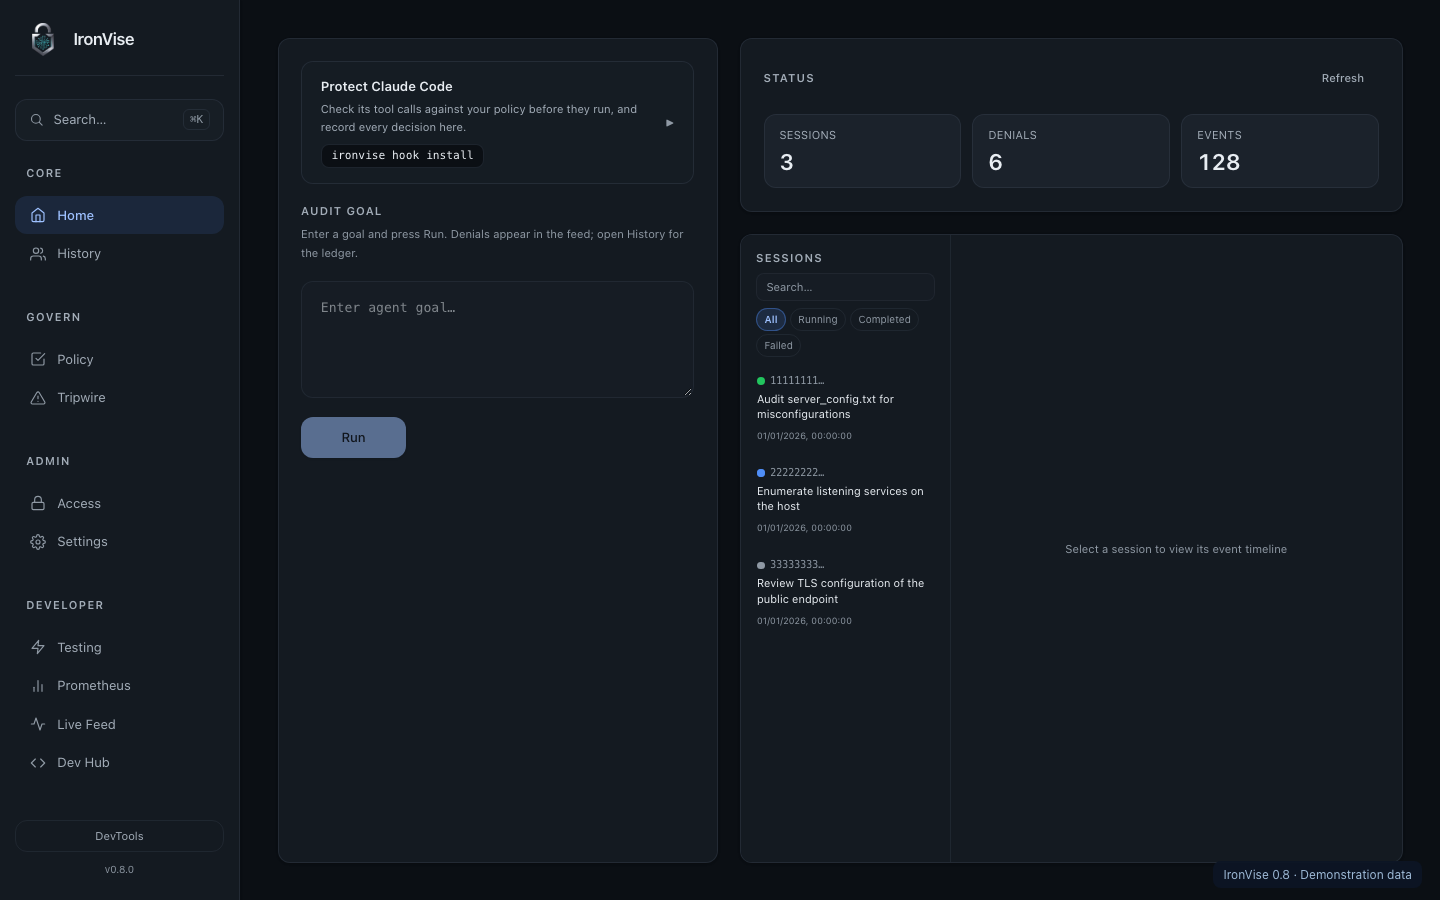
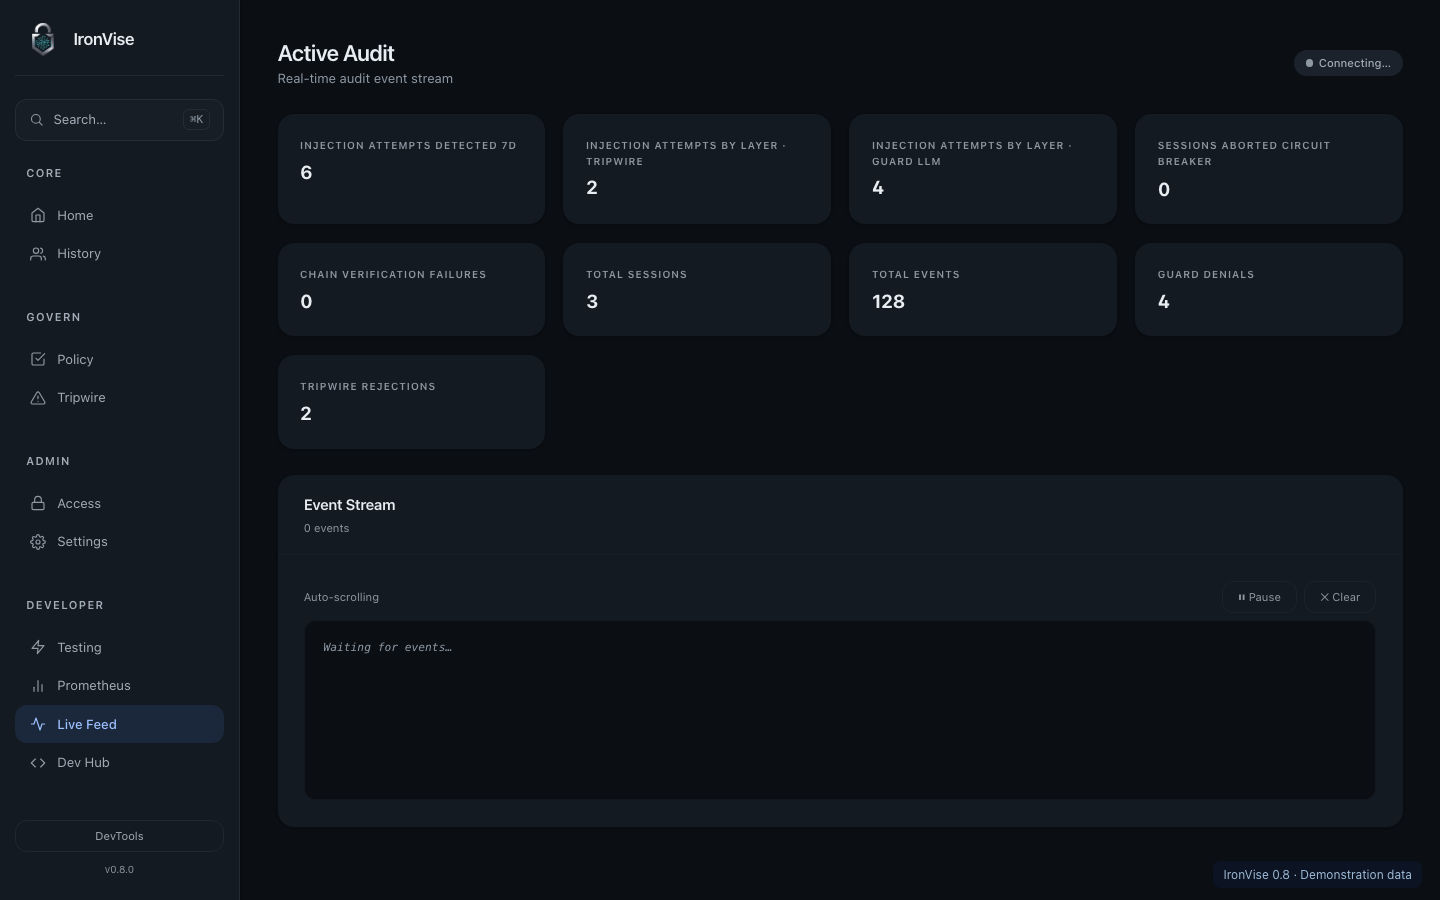
Explore recorded actions, policy decisions, data receipts, and verification in the current interface. This walkthrough uses demonstration data.
Who is this for?
EU AI Act timelines are approaching. IronVise gives you auditable evidence for high-risk AI workflows now.
If your agents run commands and APIs, you need a provable trail showing every decision and action.
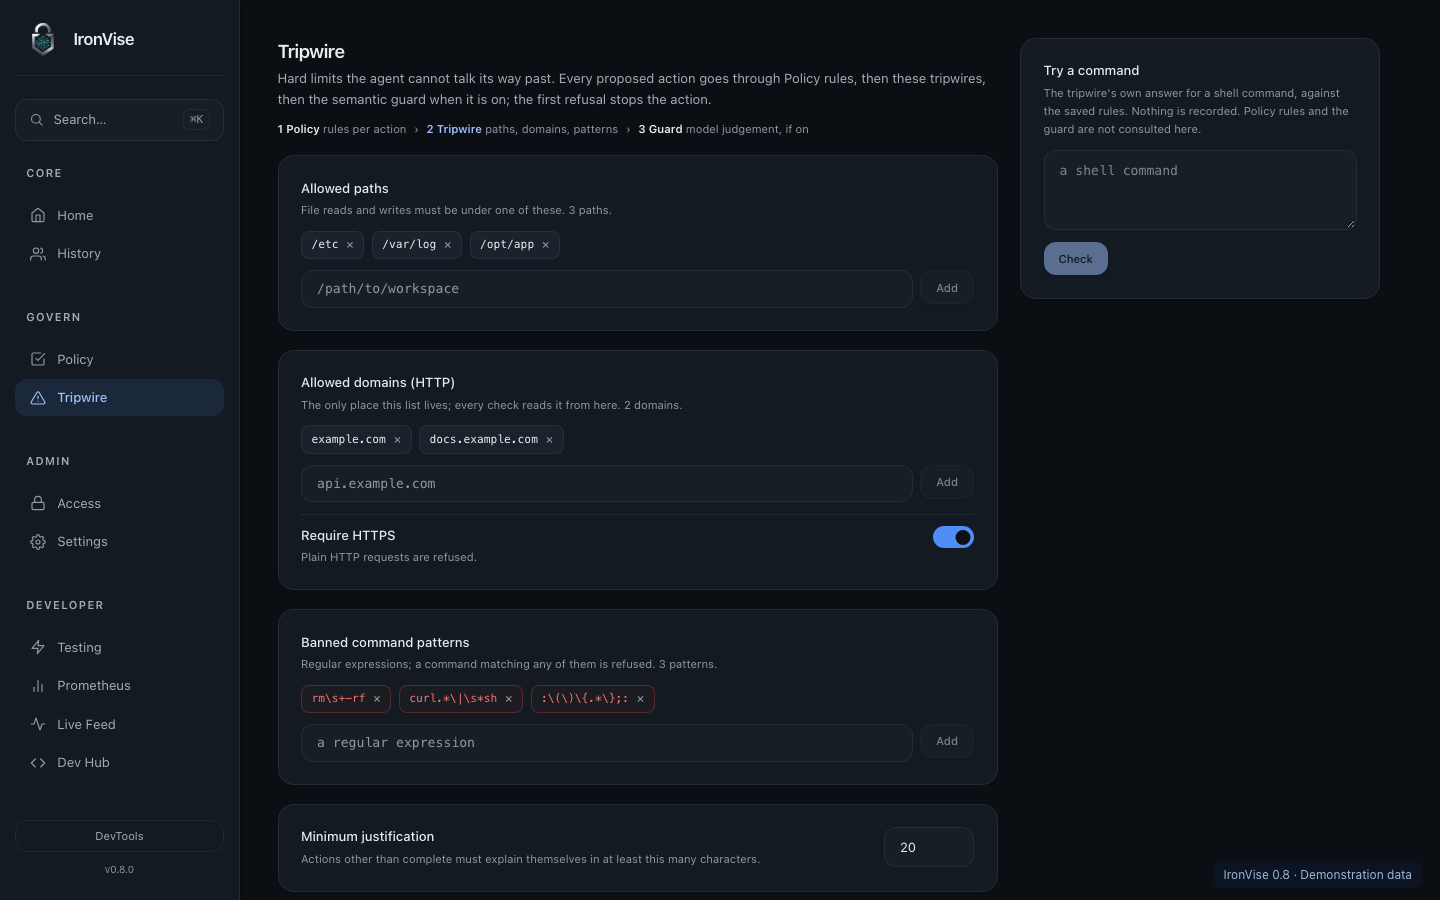
Every action passes four validation layers before execution. Rejections are logged and reviewable.
Export .elc certificates and verify them offline with a standalone binary. No vendor trust required.
The Solution
Core Ledger
Capture every model decision, tool action, and operator approval in a timeline you can replay and verify.
4-layer semantic guard
Policy engine, strict schema validation and Tripwire check every proposed action; the dual-LLM semantic guard adds a fourth layer when it is turned on. An action that fails a layer is blocked before it runs.
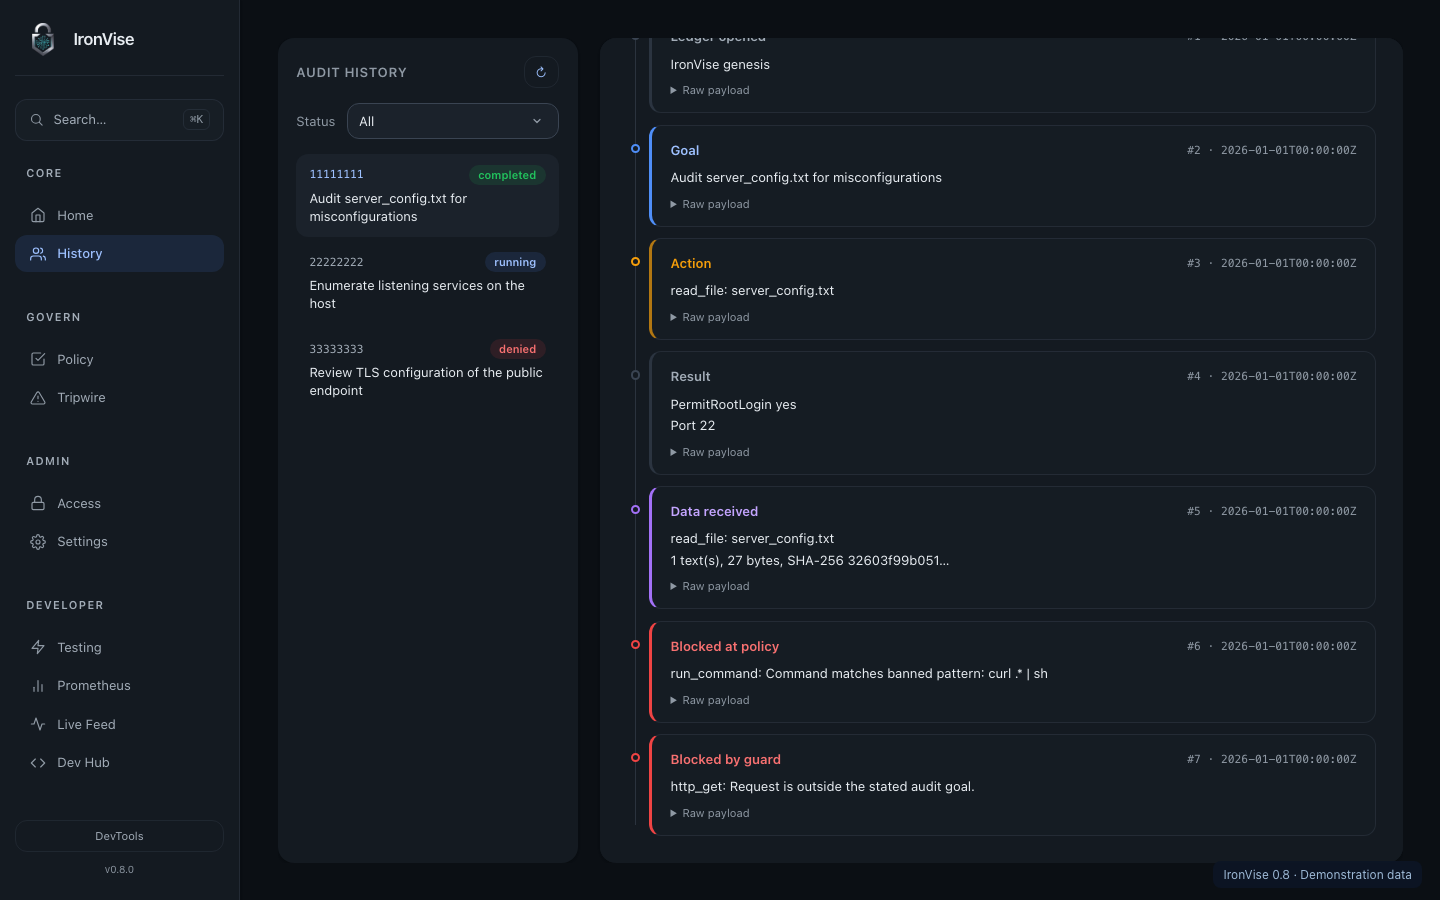
.elc audit certificates
Export a self-contained certificate with cryptographic proofs and verify it offline using the standalone verify-cert binary.
Legal admissibility depends on jurisdiction and process; IronVise provides cryptographic evidence to support review and testimony.
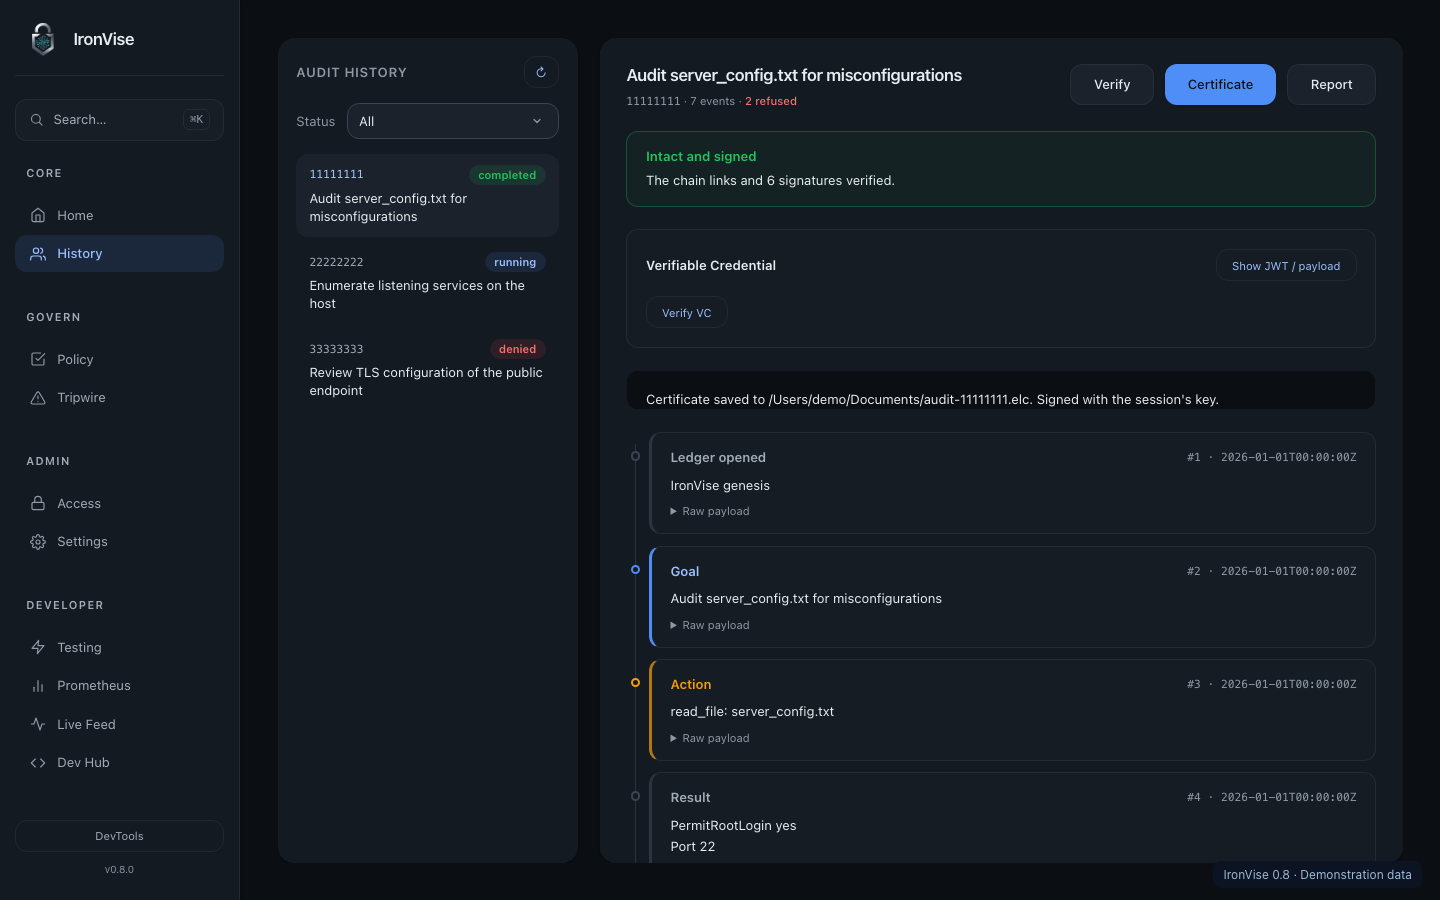
Policy Studio
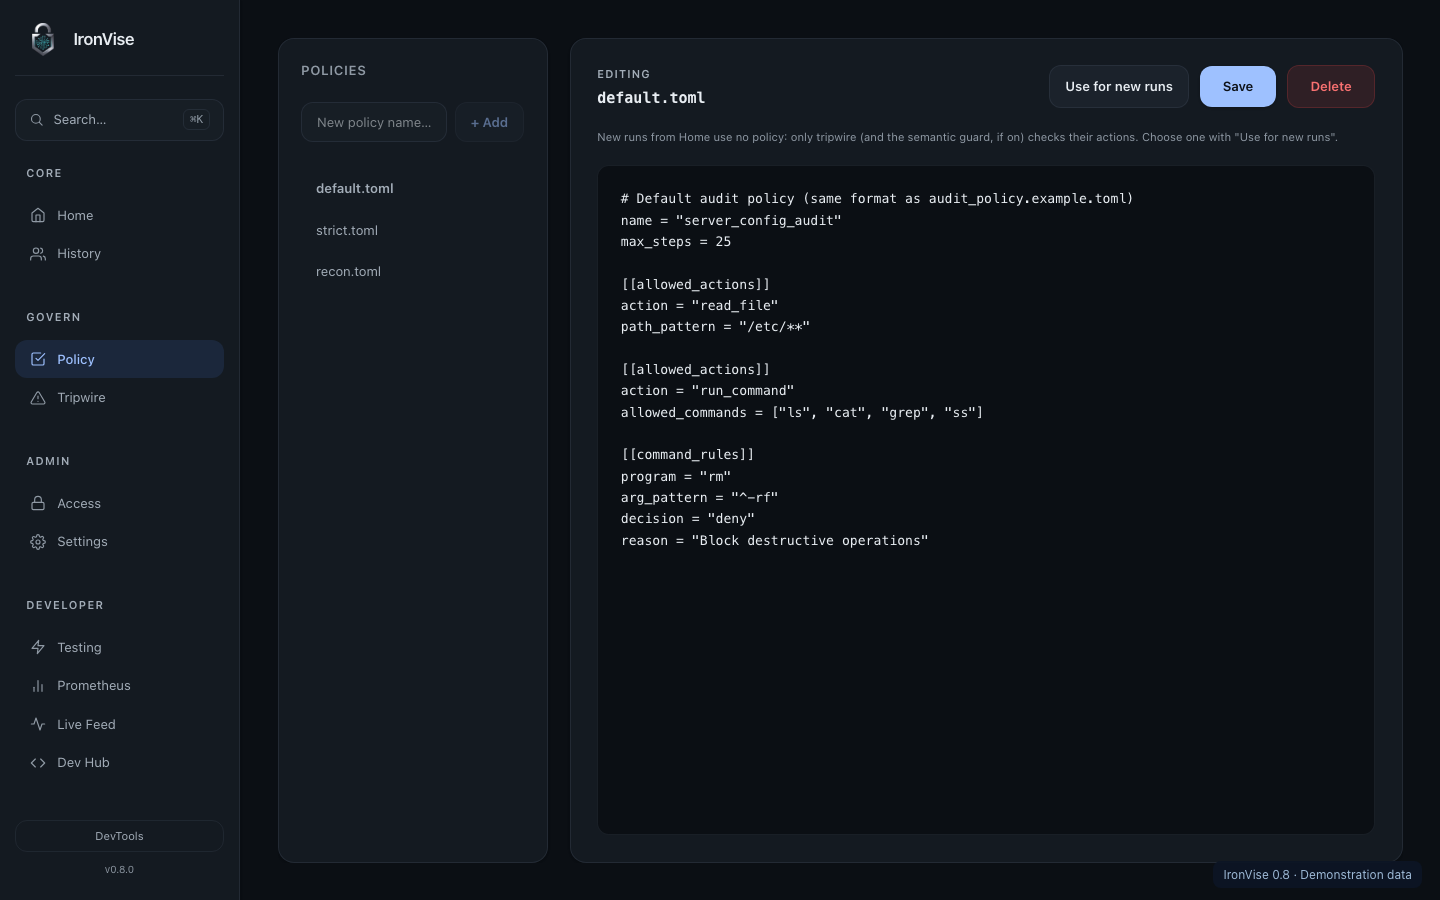
Metrics
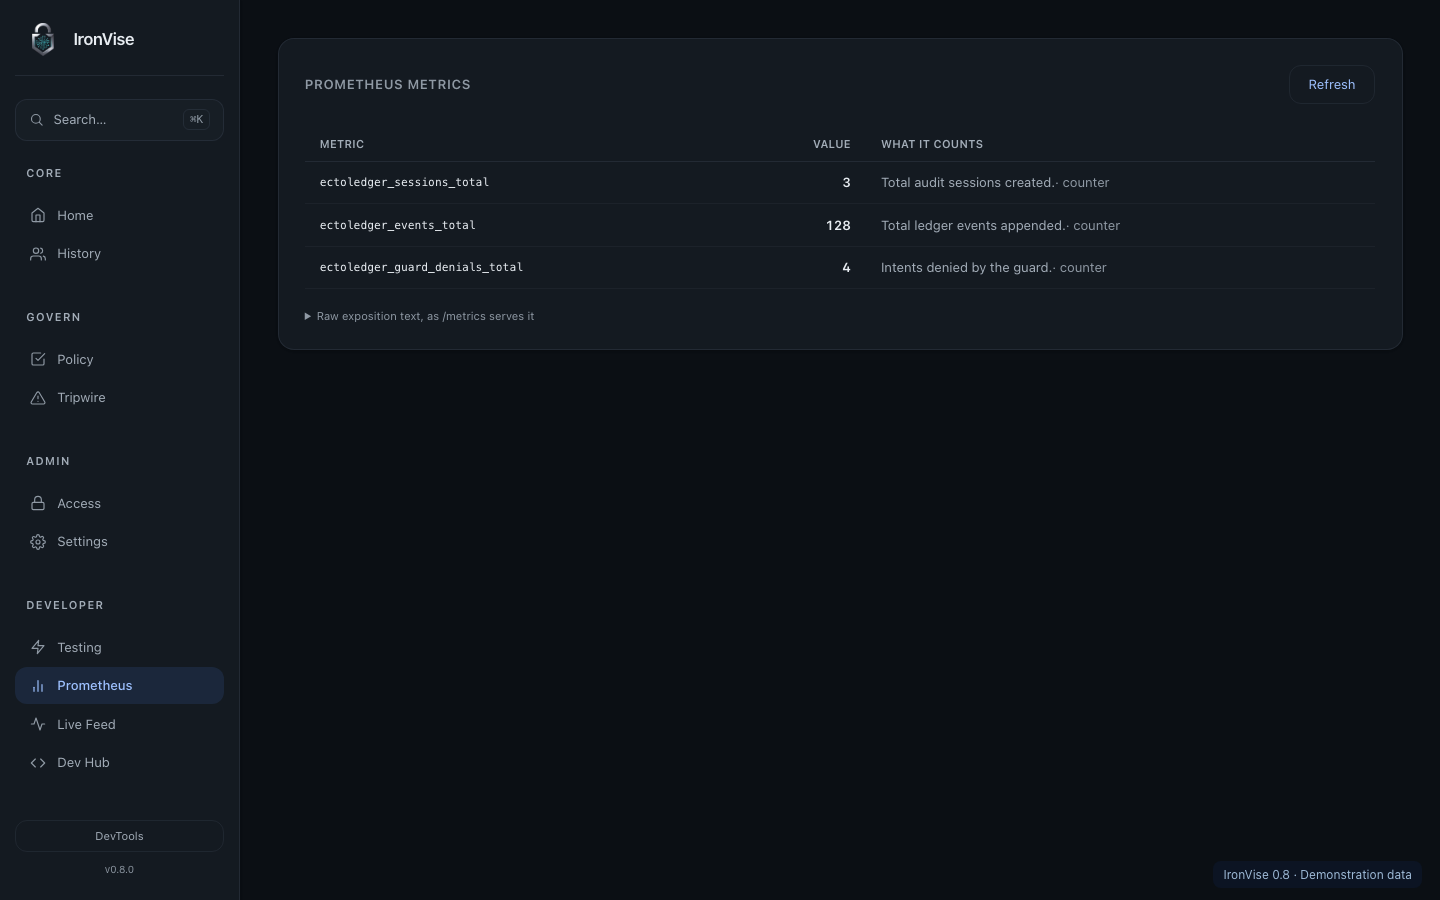
Active Audit
Philosophy
The Rust process is a transient worker. All durable state - event log and snapshots - lives in the configured backend (PostgreSQL or SQLite). The binary has no long-term memory; it restores state from the ledger on each run.
Proposed actions from the LLM are never trusted directly. Policy engine, guard process, then Tripwire validate every intent before commit. Intents that pass are appended to the hash-chained ledger and executed; nothing is ever updated or deleted.
Industry policy packs
SOC 2, PCI DSS v4.0.1 and OWASP Top 10 rule packs: load one with --policy crates/host/policies/soc2-audit.toml, or choose it for runs in the desktop app. ISO 42001:2023 ships as a controls mapping.
How It Works
The workflow follows a deterministic progression designed for high-assurance environments.
Step 1
Create a scoped session with explicit mission and policy boundary.
Step 2
Append model and tool events while guardrails validate each operation.
Step 3
Seal the session and export verifiable certificate artifacts.
Execution health
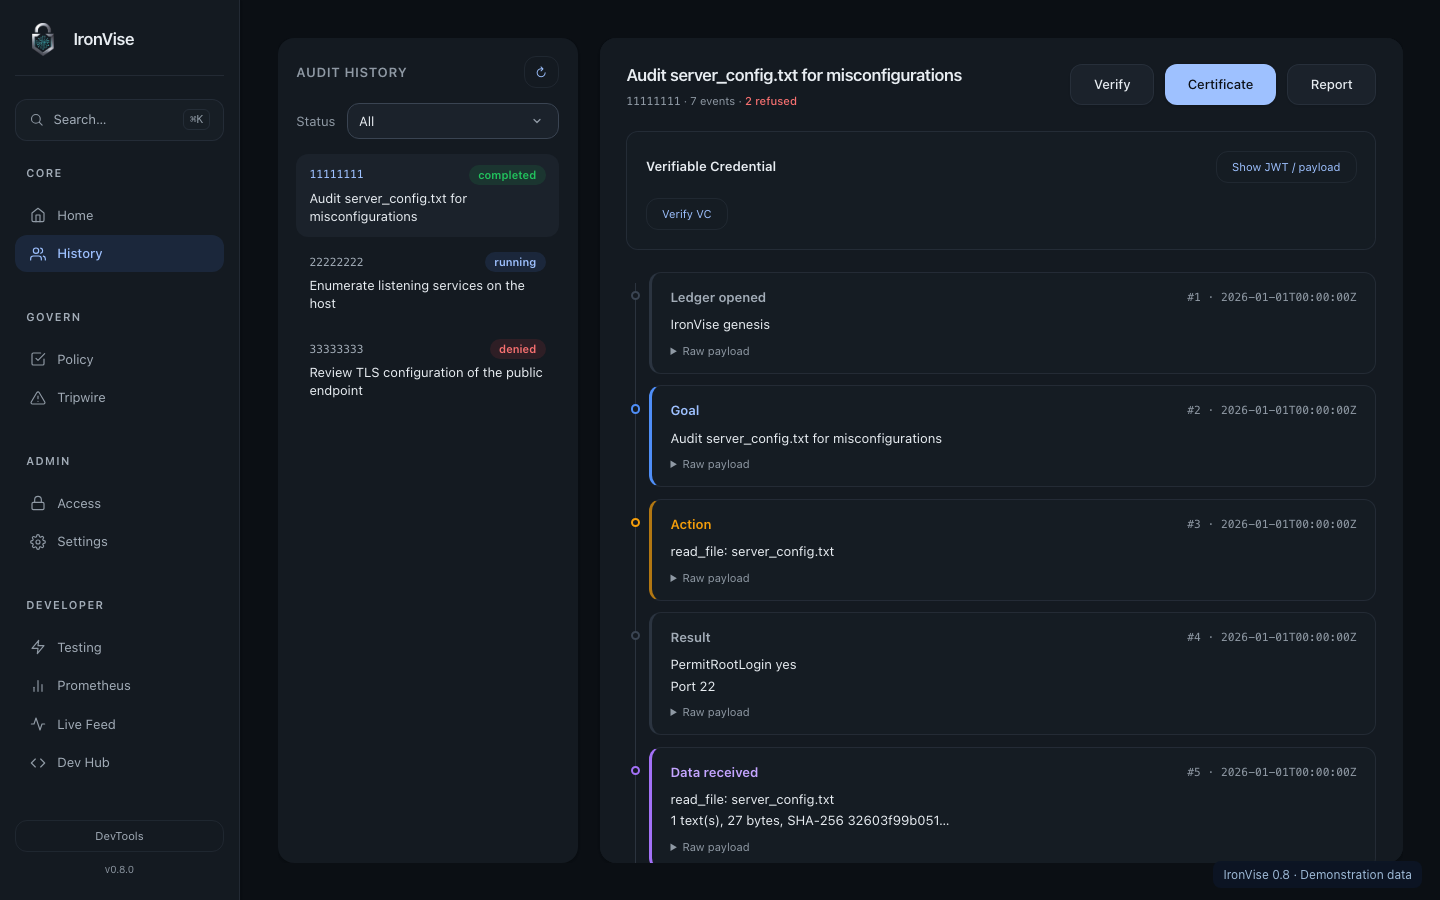
How-To
GUARD_REQUIRED=true.audit \"<goal>\", then export and verify .elc..elc certificate.verify-cert.Need help with setup or verification errors? See the Troubleshooting guide.
v0.8.0 · Release notes
New in v0.8: security hardening, an honest desktop first-run path, and a shorter GUI. Full README and CLI reference live on GitHub.
ECTO_SANDBOX_PERMISSIVE opts back out.read_file refuses to follow a leaf swapped for a symlink between validation and open, with regression tests for the race window.make start, make demo, and the Docker demo all verified from a clean checkout.DATABASE_URL; LedgerBackend trait for custom stores.did:key: anchored.run_command (Linux, guest image you supply).verify-cert binary.Developers
Zero-friction setup: make targets on macOS/Linux, a PowerShell launcher on Windows, a Docker demo, or SQLite for local dev. Full docs on GitHub.
Clone, then make start for the desktop GUI - it runs its own backend in-process. Or make demo for a zero-config SQLite dashboard with no Docker or PostgreSQL.
make startmake demo.\ironvise-win.ps1docker compose -f docker-compose.demo.yml upServe dashboard, run audits, export reports and certificates.
serve - Observer dashboard (default http://localhost:3000)audit "<goal>" - Run cognitive loop with policy/guardreport <session_id> --format certificate --output audit.elcverify-certificate audit.elc - Offline .elc verificationorchestrate "<goal>" - Recon → Analysis → Verifyanchor-session <id> - OpenTimestamps timestampred-team --target-session <id> - Adversarial testingprove-audit <id> - unavailable in 0.8; use certificate exportpip install ironvise installs the Python SDK. Optional extras: [langchain] or [autogen]. sdk/python
import asyncio
from ironvise_sdk import LedgerClient

async def main():
    async with LedgerClient("http://localhost:3000", bearer_token="<token>") as client:
        session = await client.create_session(goal="Audit Cargo dependencies", record=True)
        await client.append_event(session.session_id, {"step": "read", "file": "Cargo.toml"})
        await client.seal_session(session.session_id)

asyncio.run(main())npm install ironvise installs the TypeScript SDK. Zero runtime deps, native fetch. sdk/typescript
import { IronViseClient } from "ironvise";
const client = new IronViseClient({ baseUrl: "http://localhost:3000", bearerToken: "<token>" });
const session = await client.createSession({ goal: "Summarise quarterly report", record: true });
await client.appendEvent(session.id, { step: "retrieved_docs", count: 42 });
await client.sealSession(session.id);
const cert = await client.exportCertificate(session.id);
Audit certificates (.elc)
Every completed session can be exported as a self-contained .elc verifiable offline. SP1 proof generation is unavailable in 0.8. Auditors can run verify-cert offline without a database, model, or Rust toolchain.
Tamper evidence; payload signed with the session keypair; no trusted third party.
Gap and mutation detection; any insertion or change is detectable offline.
Efficient finding spot-checks; O(log n) verification per finding.
Timestamping; once the OpenTimestamps stamp is upgraded, proves the session existed before block N.
Session integrity; goal cannot be redirected mid-session.