Audit command fails
- Confirm backend mode supports your command.
- Check primary LLM connectivity and API keys.
- Verify guard settings when running production mode.
See IronVise in action
IronVise records every AI decision, blocks unsafe actions before execution, and produces tamper-evident certificates you can verify offline.
Before you start
Demo mode is optimized for fast evaluation. For production use, configure guard, policy, backend, and webhook settings explicitly.
Before you run demo
What you need depends on how you run the demo. At minimum, choose one path below.
docker-compose.demo.yml). Not required for make demo, SQLite, or embedded PostgreSQL.audit and orchestrate the primary LLM must be reachable; the Guard uses GUARD_LLM_BACKEND / GUARD_LLM_MODEL when GUARD_REQUIRED=true.gui/). The Docker demo exposes the REST API and Observer only; no GUI.How to use demo mode
You can try IronVise with zero config (embedded Postgres, auto LLM detection) or use Docker for a fully containerized stack.
Demo defaults prioritize fast evaluation. Before production rollout, explicitly configure guard, policy, backend mode, and webhook settings.
make demo (zero config)
Starts the Observer dashboard against a local SQLite ledger with ECTO_DEMO_MODE=1. No Docker, no PostgreSQL, and no API key required - the ledger file is created on first run.
# macOS / Linux
make demo

# Windows (PowerShell)
.\ironvise-win.ps1 -demo
Equivalent to ECTO_DEMO_MODE=1 DATABASE_URL=sqlite://ectoledger-demo.db cargo run --release -p ectoledger -- serve. The ledger lives in ectoledger-demo.db in the repository root; delete that file to wipe demo data. Demo mode is insecure by design - see running securely before any real deployment.
make start (desktop GUI)
Runs the Tauri desktop app, which starts its own Observer backend in-process - no separate server to manage. Uses your configured DATABASE_URL and LLM. Good for development and real audits. Use make backend for the server alone.
make start # macOS / Linux - Windows: .\ironvise-win.ps1
One command pulls the pre-built image and starts PostgreSQL 17, Ollama, and IronVise. Open http://localhost:3000 for the Observer dashboard. No Tauri GUI in Docker - use make start for the full desktop experience.
docker compose -f docker-compose.demo.yml upTo reset: docker compose -f docker-compose.demo.yml down -v
serve (no Docker)
For a local dashboard or CLI audit with no external database, set DATABASE_URL=sqlite://ledger.db and run cargo run -- serve (or audit, report, verify-session, anchor-session). Only multi-agent orchestrate, diff-audit, and red-team require PostgreSQL.
Full details: Zero-Config Demo and Demo Readme on GitHub.
Troubleshooting
verify-cert validates certificate evidence offline.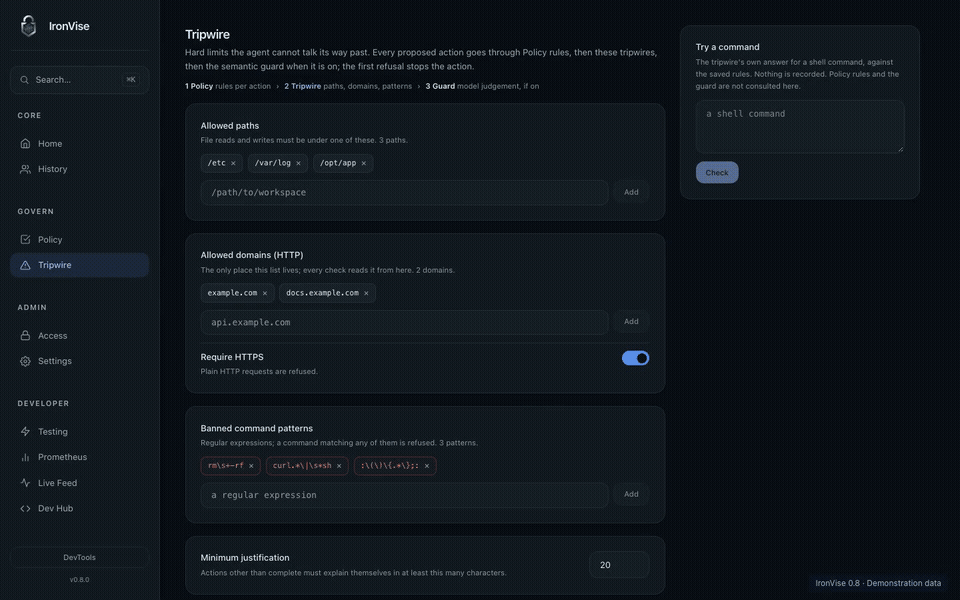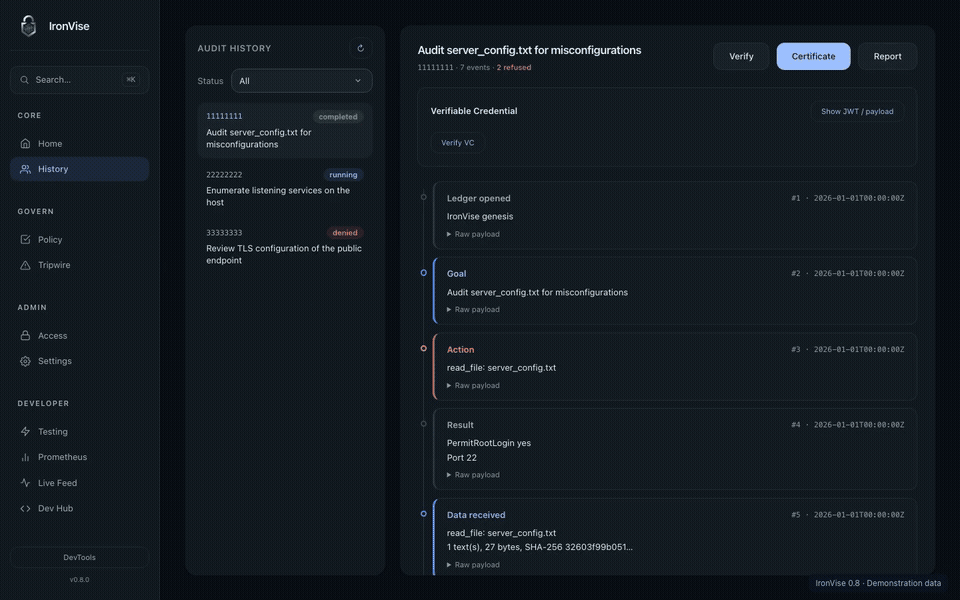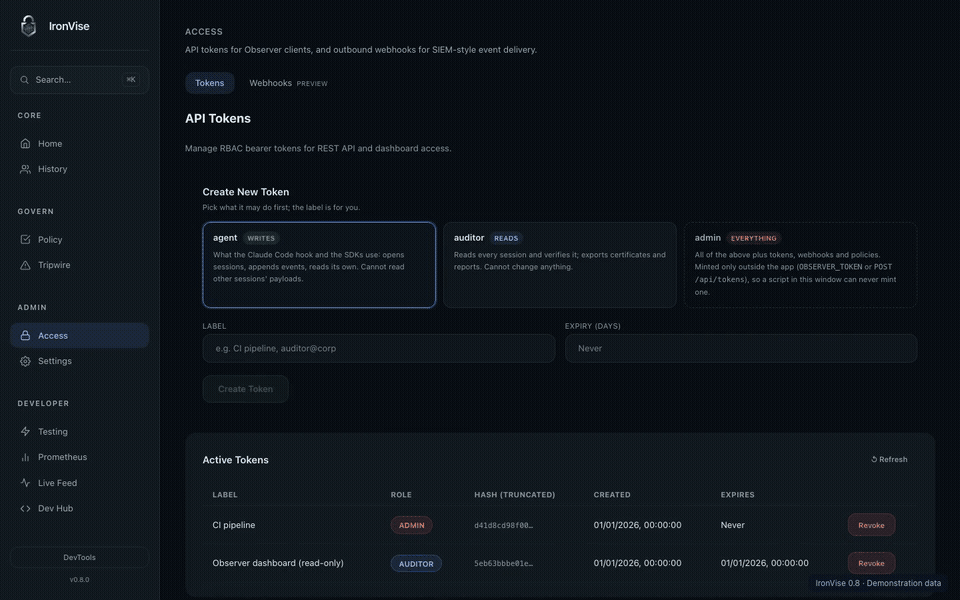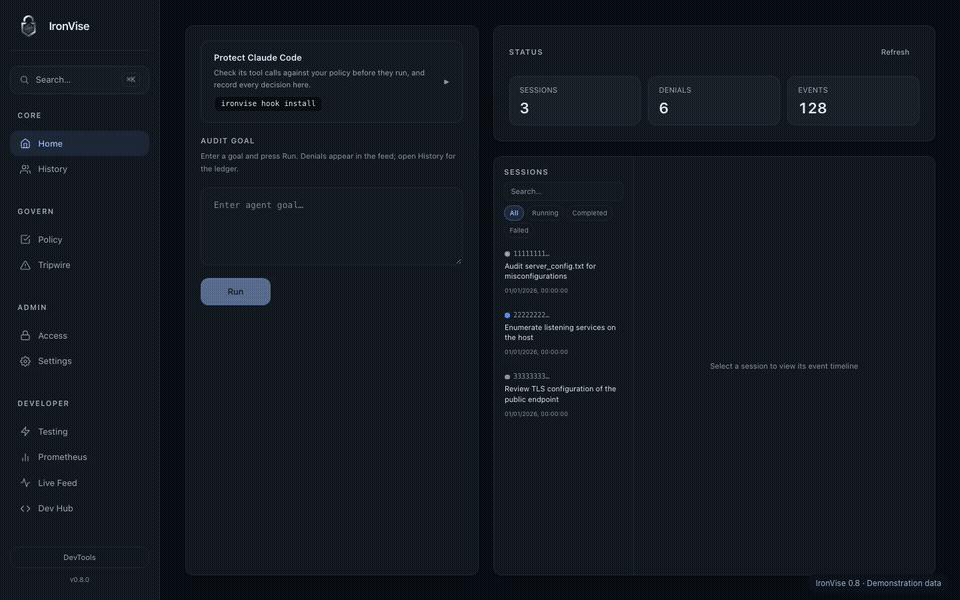
Feature Clips
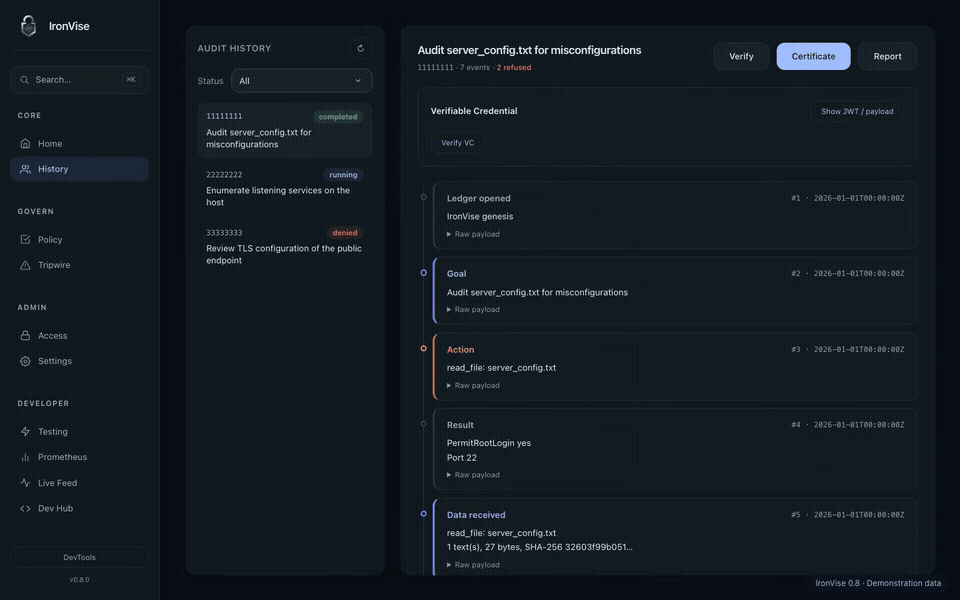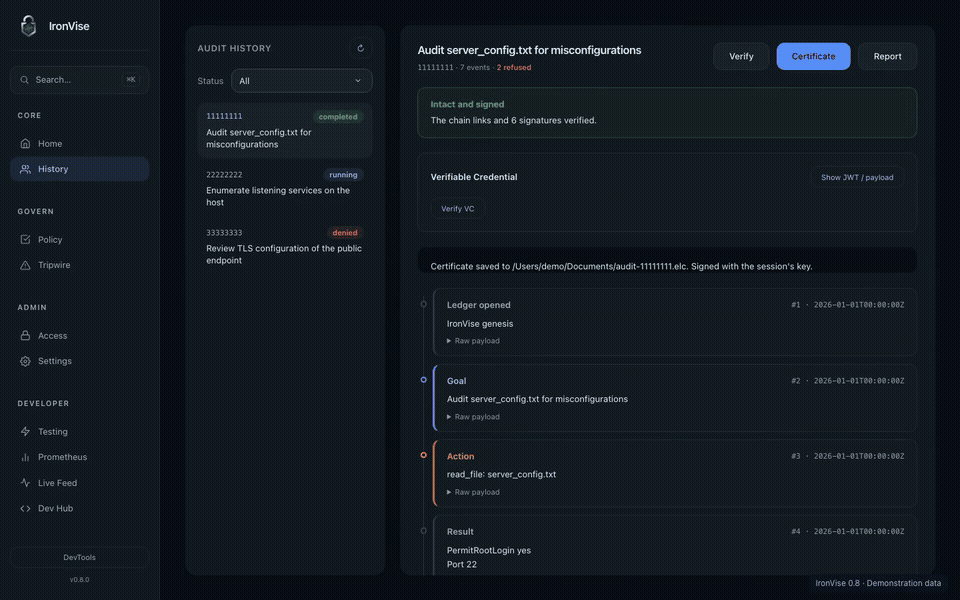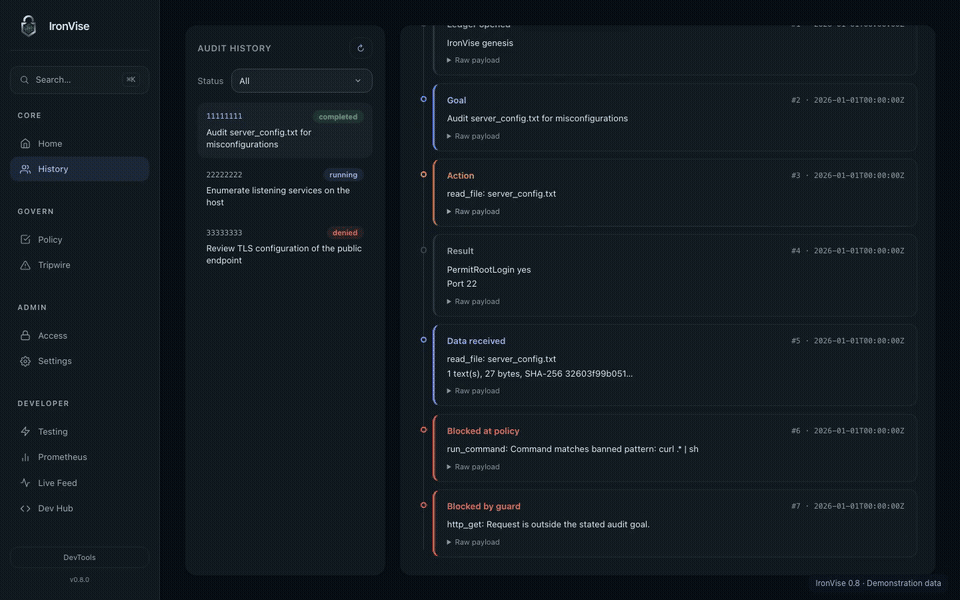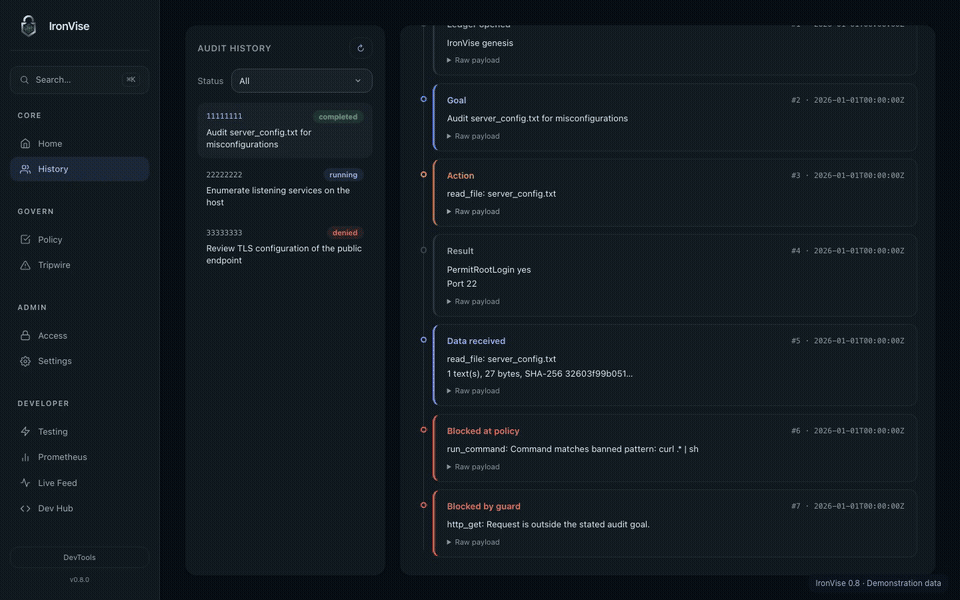
Walk through recorded actions, decisions, and verification using demonstration data.
Inspect example policy decisions, data receipts, and session verification in IronVise 0.8.
Interface walkthrough
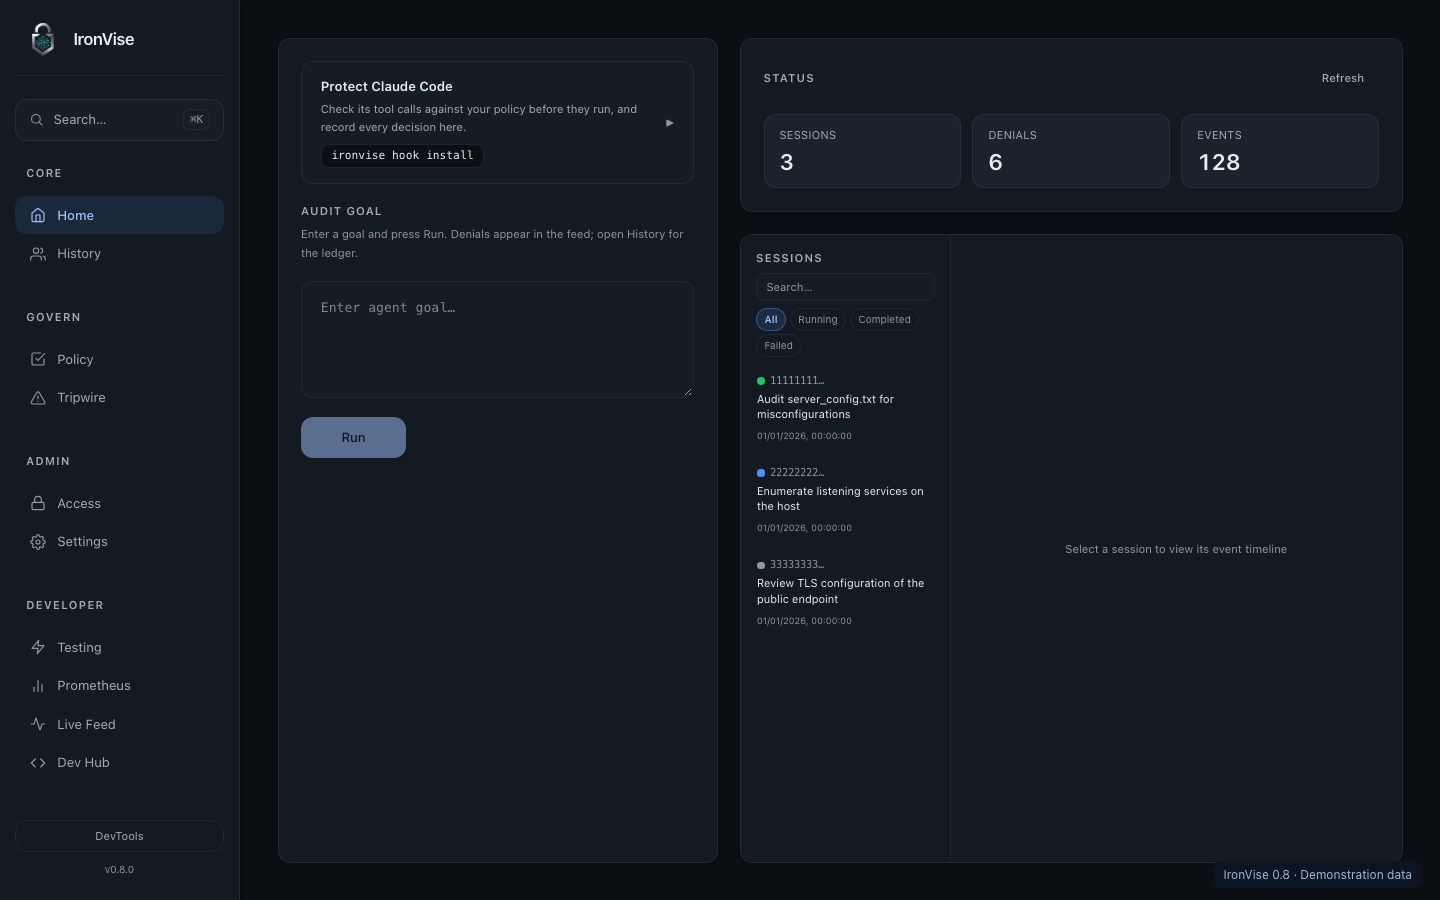
Give your AI agent a task and watch every decision get recorded.
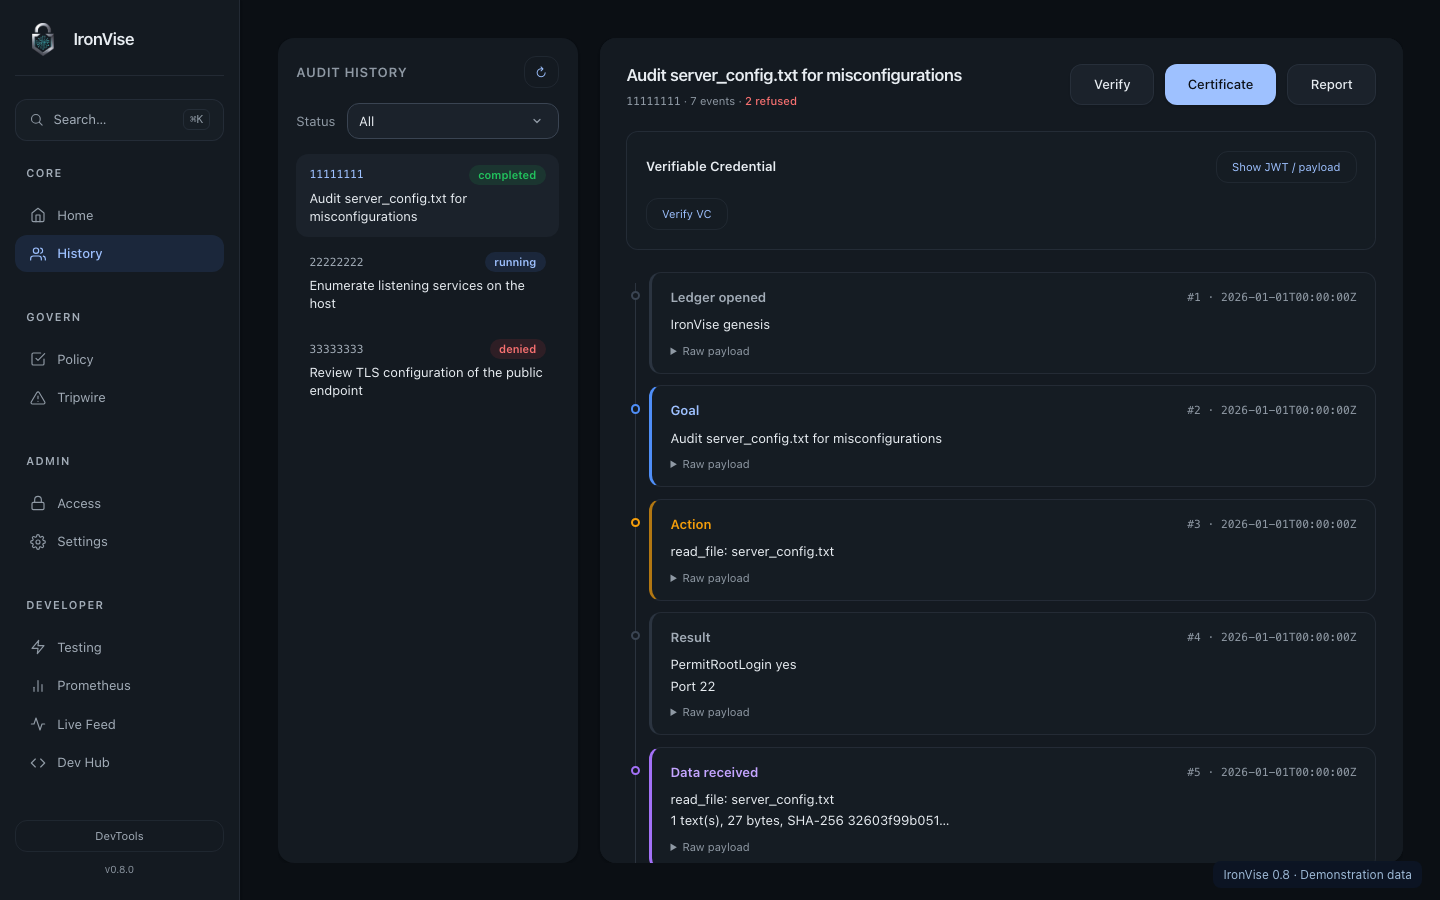
Review exactly what your AI did, step by step.
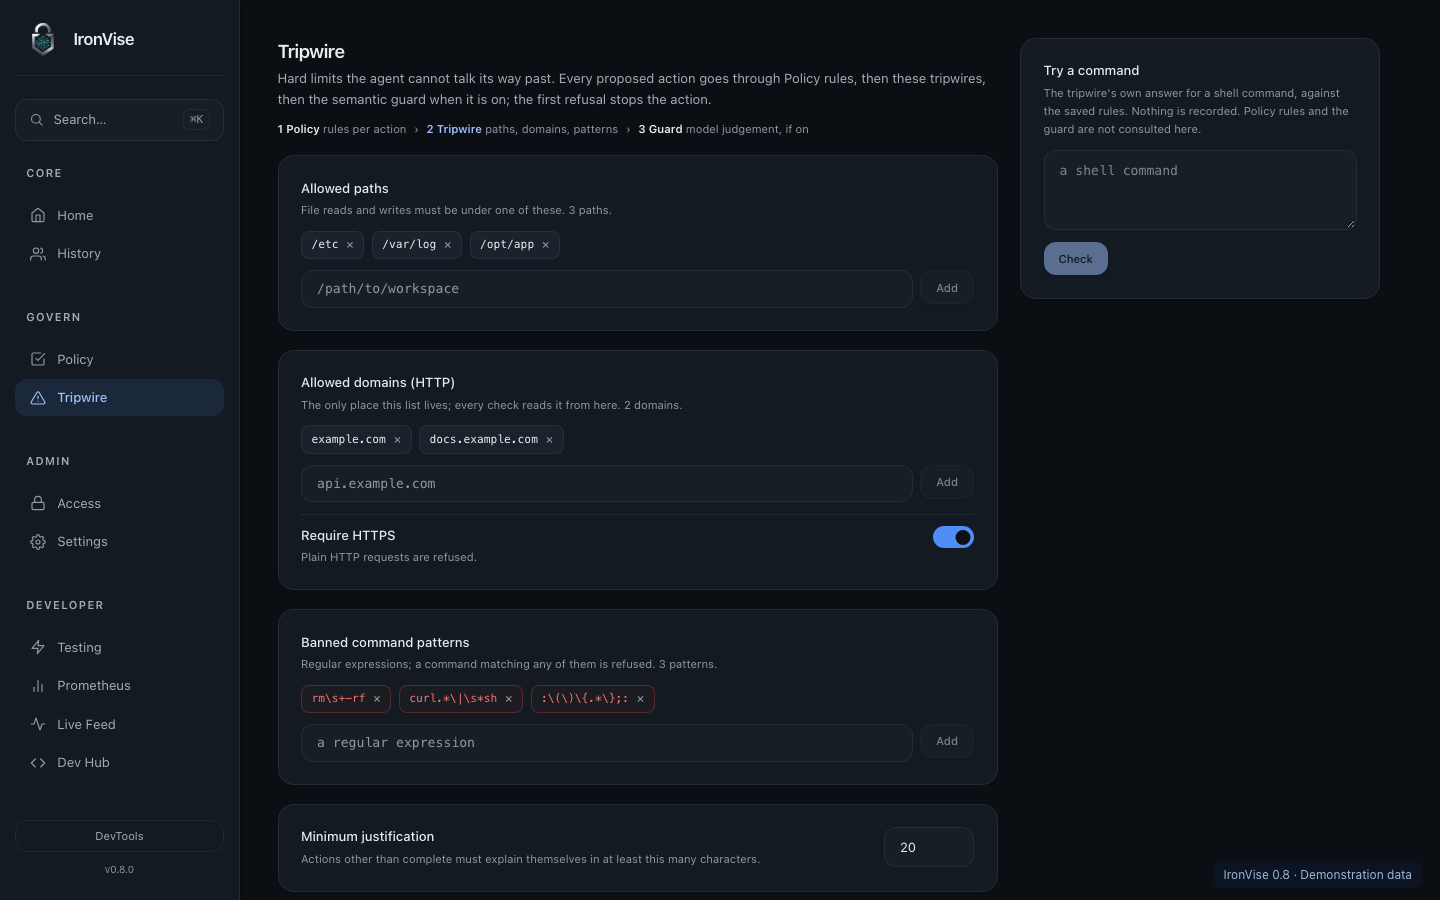
Define boundaries your AI cannot cross.
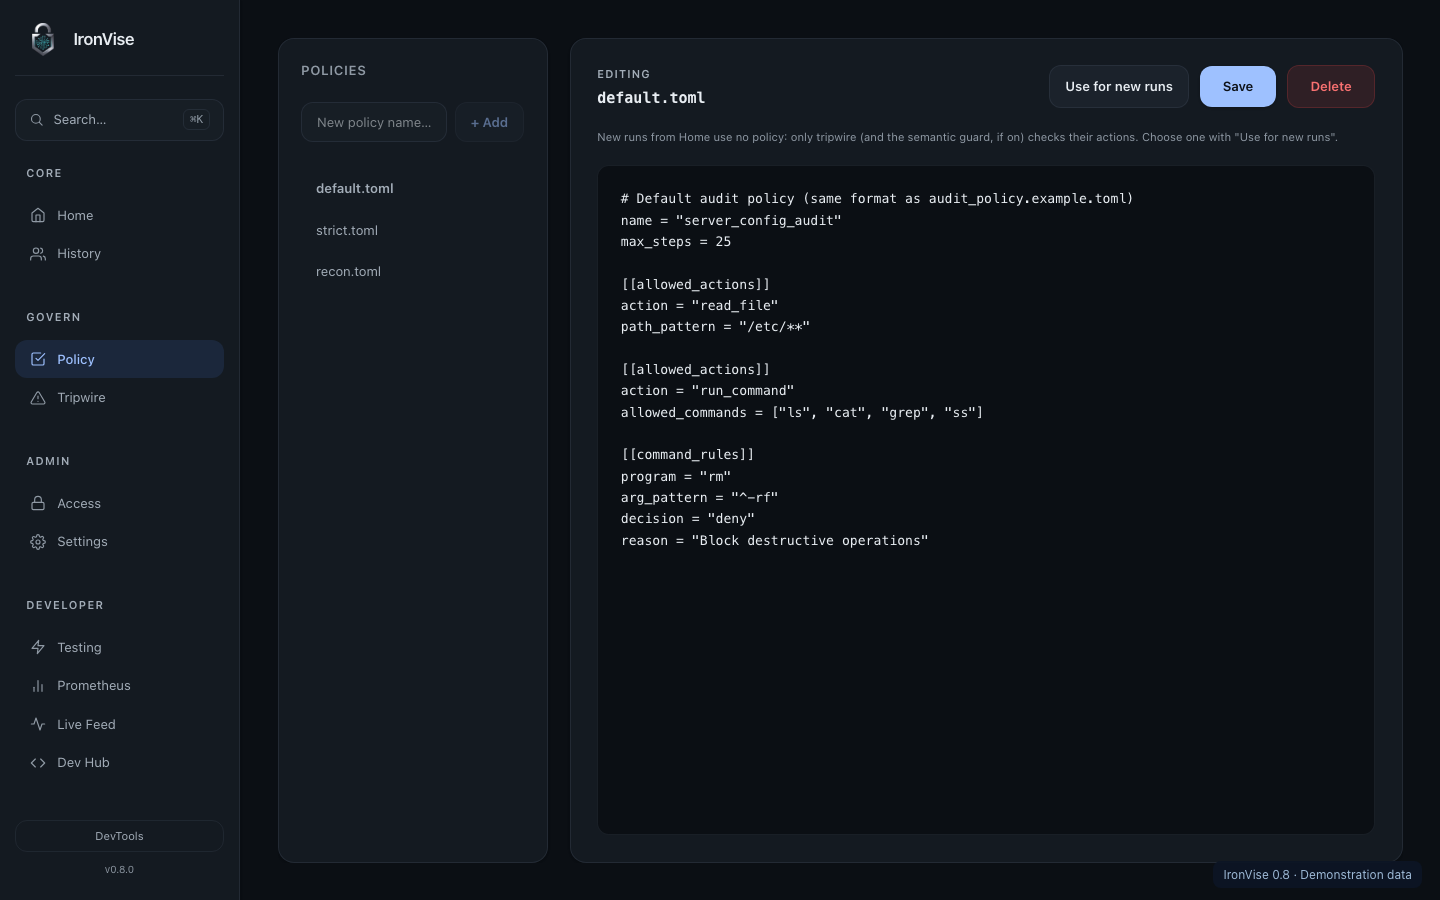
Write rules that govern what your AI is allowed to do.
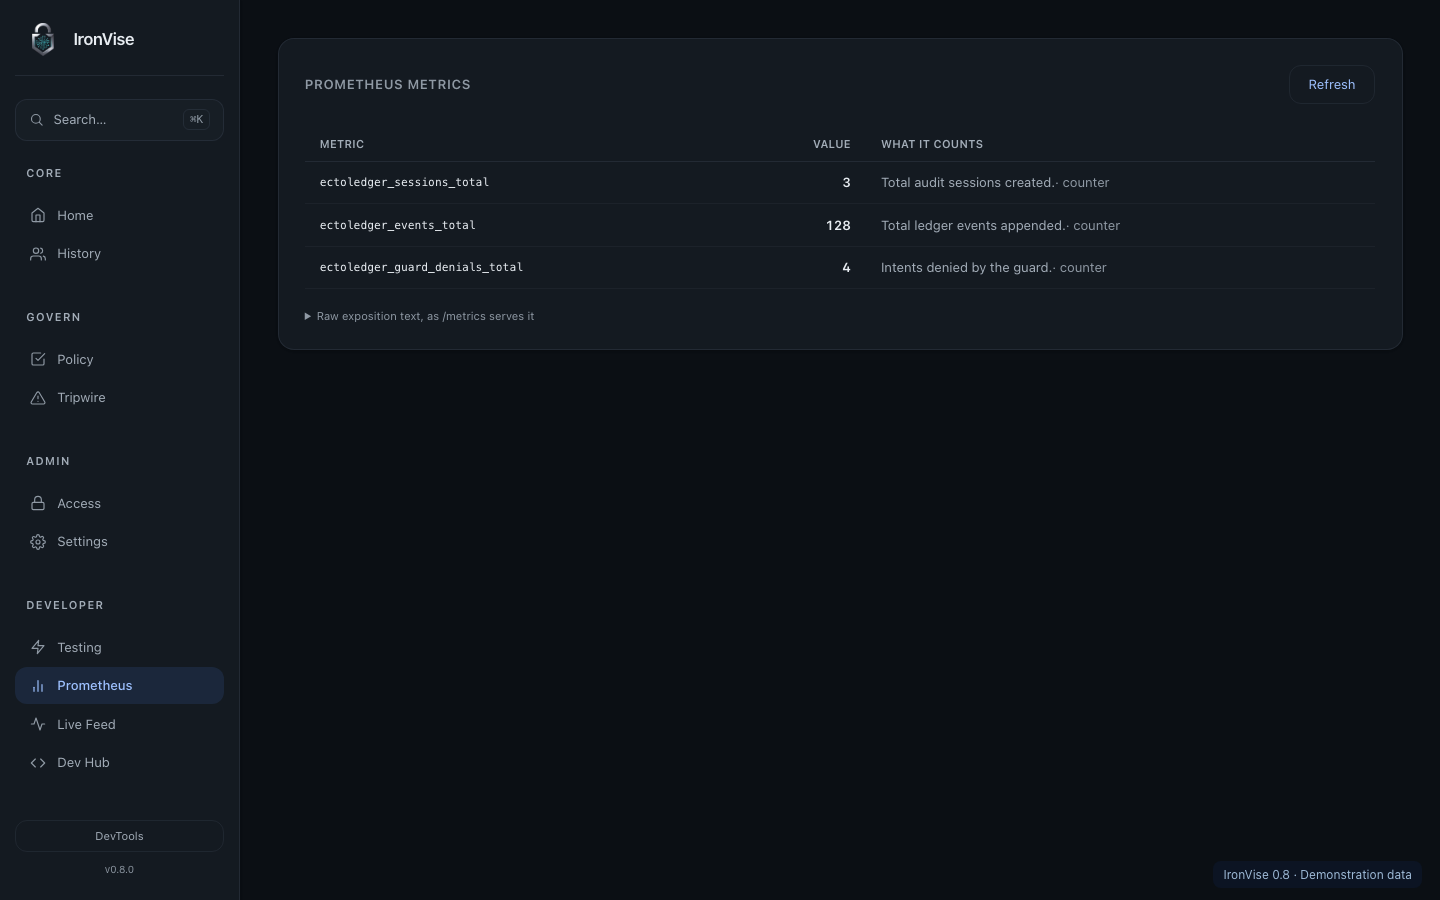
Monitor AI agent behavior and reliability in real time.
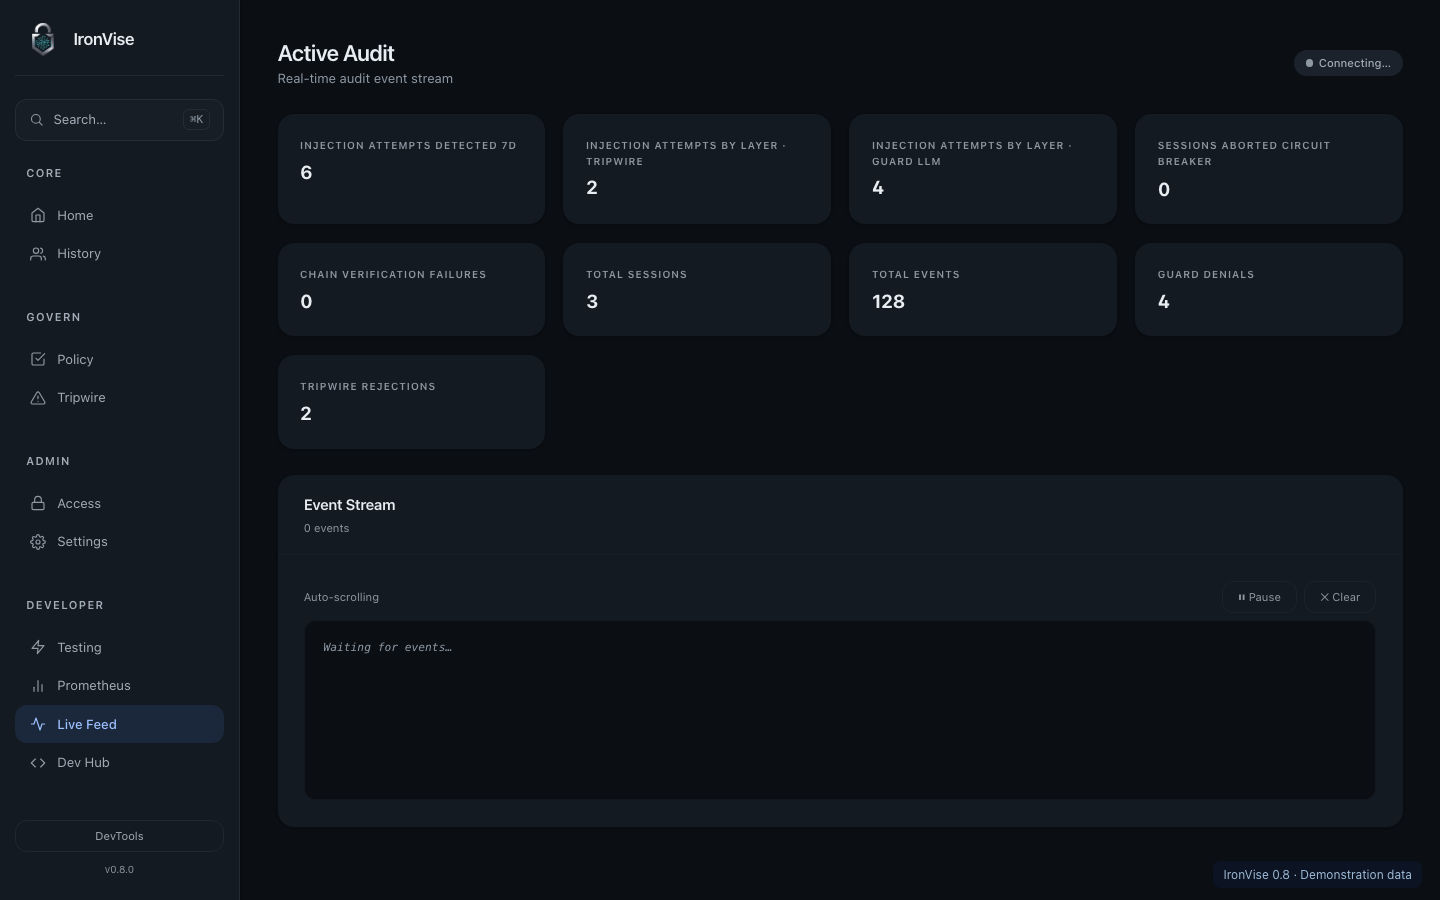
Watch the pre-execution checks evaluate each action as it happens.
Next step
Start with Quick Start for setup, or review the latest release notes before integrating IronVise.